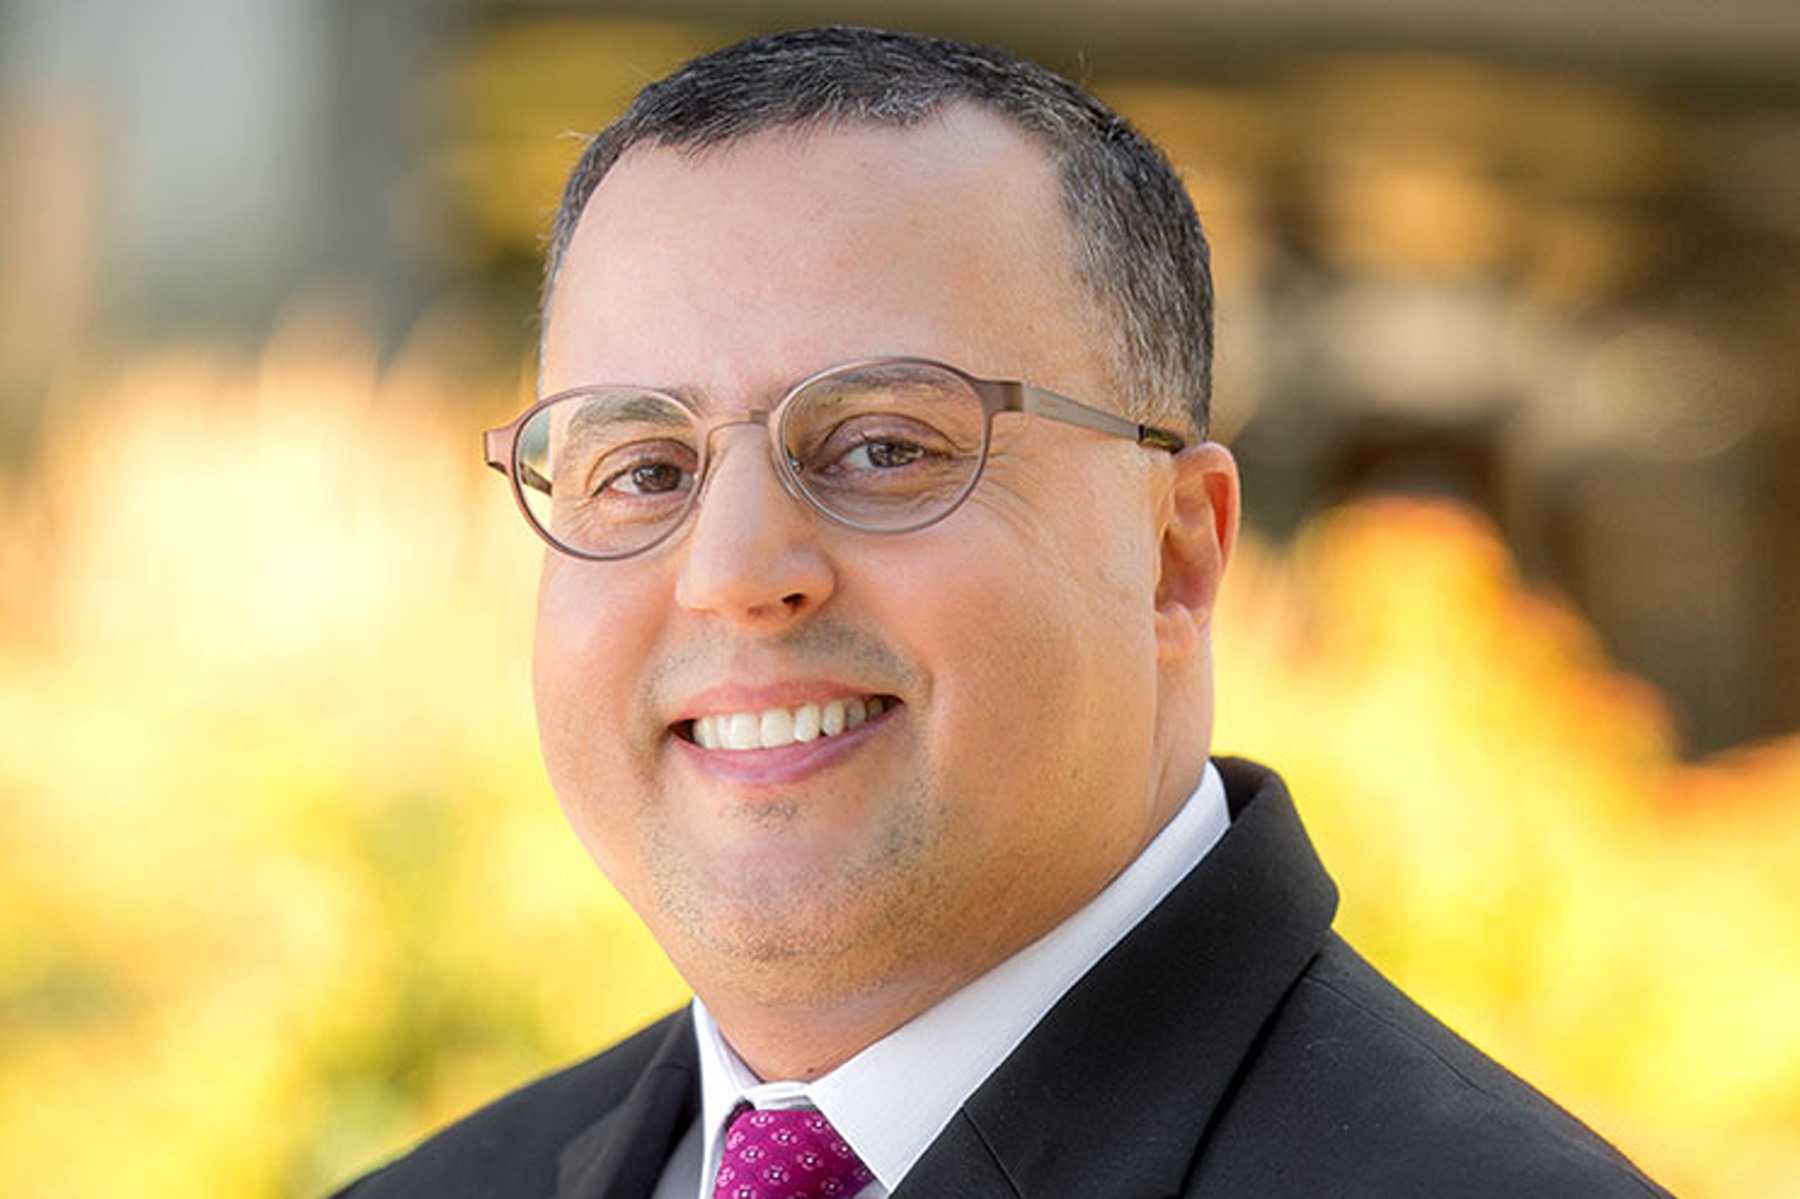
With a career built at companies like Visa, Ellie May, and Blackhawk, Selim Aissi, a 2026 CSO hall of fame inductee, understands how boards and executives demand a clear justification for cyber security investment, especially considering today’s difficult economic climate.But getting security leaders to communicate tec…
With a career built at companies like Visa, Ellie May, and Blackhawk, Selim Aissi, a 2026 CSO hall of fame inductee, understands how boards and executives demand a clear justification for cyber security investment, especially considering today’s difficult economic climate.But getting security leaders to communicate tec…
A lot of organizations add tools, and more platforms and controls in response to new threats. Yet that doesn’t necessarily address underlying complexities. Security investment can actually increase operational and strategic risk.
“I think there’s a tipping point once a reasonable depth of defense is in place,” he says. “When there’s a reasonable level of automation of security controls and cross integration of security tools, anything beyond that could potentially be overspend and could potentially add risk to the entire organization.”
So the challenge is to know when an environment exists and functions without the need for a sudden budget spike.
“All of the KRIs and KPIs in place should be able to indicate the level of resiliency,” he adds, “in addition to other controls such as making sure there are processes that would allow for detection of, let’s say, API abuse, cloud-level abuse, and, increasingly these days, AI as it adds yet another threat vector.”
Understanding risk also lies in recognizing the distinction between organizations that are genuinely resilient, and those that appear mature on paper, focused on fine-tuning policies, compliance, governance, and frameworks.
In context
- Topic: Ciberseguridad — Riesgo, identidad, respuesta a incidentes y cumplimiento.
- Source: CIO
- Published: 14/10/2026
Continue reading at the original source →
Excerpt published automatically by the site radar. The full text belongs to its publisher and is linked above.
Por que importa
Em segurança, a notícia quase nunca é o ataque: é o tempo entre a invasão e alguém perceber. Esse número diz mais sobre uma organização do que qualquer certificado pendurado na parede da recepção.
Minha forma de olhar esses casos é perguntar o que falhou no processo, não o que falhou na máquina. Atrás de quase todo incidente há uma decisão razoável tomada sob pressão: dar uma permissão para desbloquear alguém, adiar uma atualização porque era fechamento de mês. A lição está ali.
O que costuma dar errado
O ponto cego mais caro costuma ser o fornecedor. Blinda-se o perímetro próprio e dá-se acesso amplo a um terceiro que não tem metade desses controles. Boa parte dos incidentes que vi na região entrou por aí, e o contrato não dizia nada a respeito.
O que observar
- Se o acesso inicial veio de uma conta legítima mal administrada, que é o padrão mais frequente.
- O que foi possível restaurar e em quanto tempo — backup que não foi testado não conta.
- Como foi comunicado a clientes e reguladores, que é onde se define o custo reputacional.
Como leio esta publicação
O que eu revisaria nesta mesma semana são os acessos: contas de gente que já saiu, permissões que cresceram sem ninguém cortar e credenciais compartilhadas que todo mundo jura que não existem. É o trabalho menos vistoso e o que mais corta ataques.
A notícia original está publicada em outro idioma; o trecho é citado como o veículo o entrega e o comentário é escrito em português.
Comentários
Ainda não há comentários. O primeiro pode ser o seu.
Está vivendo isso na sua equipe?
Abra o chat e me conte como estão lidando com isso. Tenho interesse em comparar notas.